

How registered company auditors report breaches
Key points:
- Registered company auditors are now required to submit breach reports to us via the ASIC Regulatory Portal (e.g. contraventions and suspected contraventions of the Corporations Act 2001).
- Although the breach reporting process has changed, there are no changes to ongoing breach reporting obligations for registered company auditors as a result of this change.
- The ASIC Regulatory Portal is designed to help auditors comply with their breach reporting obligations. Portal features also include:
- a record of previous breach reports
- the ability to track the status of submitted breach reports
- the ability to correspond with ASIC online about submitted breach reports.
This page provides information to assist with submitting breach reports in the portal. For information on how to use the portal, refer to FAQs: Regulatory Portal.
Key information to provide when submitting breach reports on the ASIC Regulatory Portal
Expand the accordions to see some of the key information you will be asked to provide ASIC as part of the breach report transaction (e.g. details about the nature, extent, remediation and rectification of the breach).
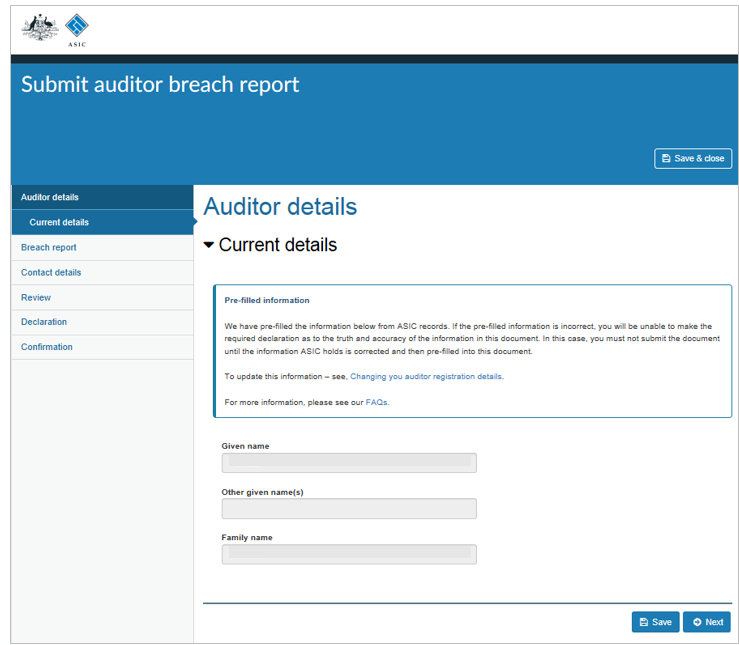
Identification
You will be required to confirm some current details – some of which will be pre-filled.
Dates
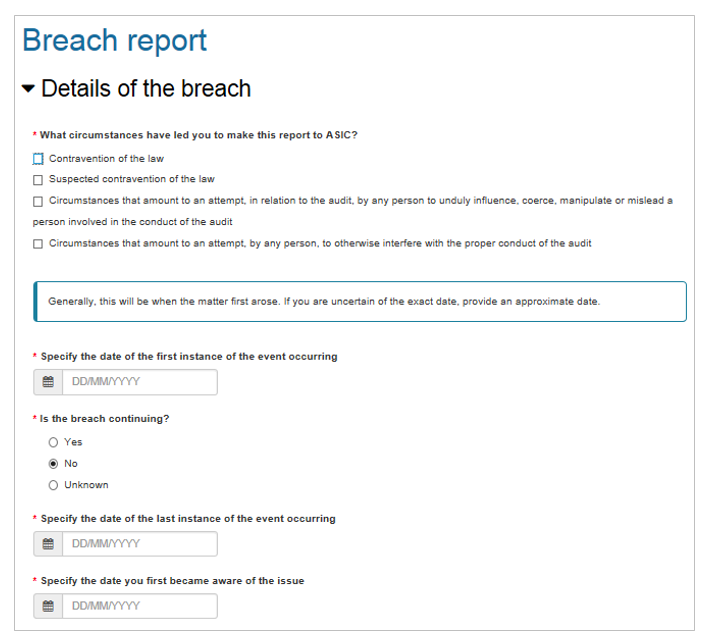
Based on your knowledge, you will be required to provide details about the date of the breach or suspected breach. Depending on the type of breach and the information you provide, you may be required to specify:
- When the breach or event first occurred.
- The last instance of the breach or event occurring.
- When you first became aware of the issue.
- Whether or not the breach is continuing.
Nature of the breach
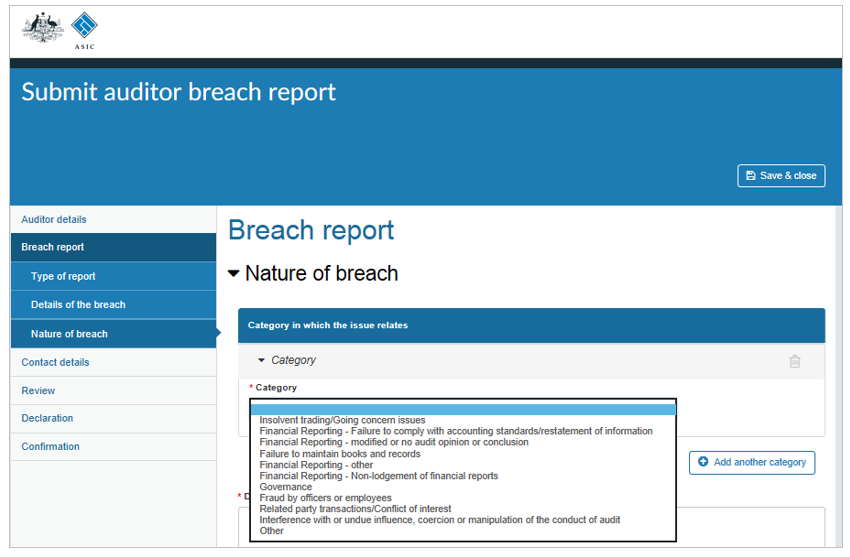
There are categories to choose from to help you describe the nature of the breach.
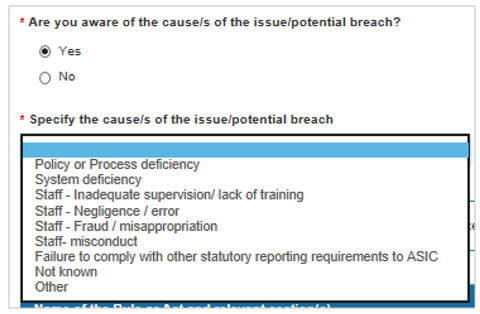
You will be asked to specify, based on your knowledge, the cause/s of the issue/potential breach.
You will need to specify the name of the Rule or Act and relevant section(s) under the Act.
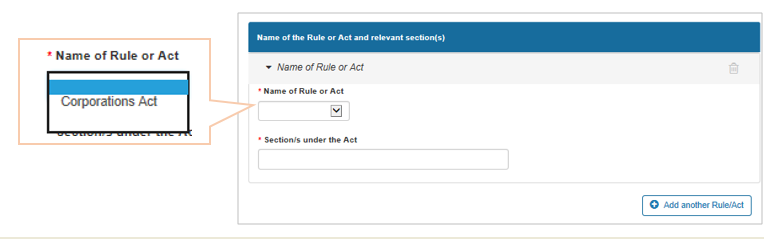
Rectification/remediation of the issue
If the organisation has rectified the issue, you will need to select how they have done so, based on your knowledge.
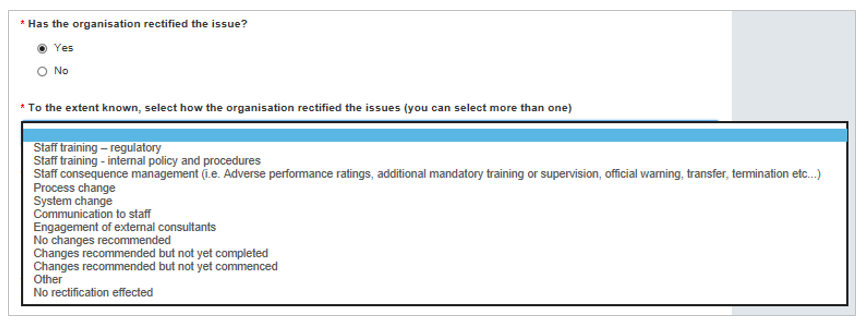
There are several other questions relating to the rectification/remediation of the issue including:
- Has the entity/licensee undertaken measures to prevent future issues form occurring?
- Are you aware of preventative measures that the auditor/entity/licensee will undertake to prevent similar issues occurring in future?
- Has the entity/licensee completed a remediation process for affected consumers (if applicable)?
- Are you aware of the date (or approximate timeframe) in which the remediation process will be completed?
Reduced need to attach supporting documentation
There will be limited requirement to attach documentation as part of the transaction. Most of the information ASIC requires will be asked for within the transaction.
Invite trusted representatives to transact in the portal on your behalf
The lead auditor or the auditor signing the audit report should submit the breach report through their portal user account.
If you would like someone to act on your behalf in the portal, you first need to invite them to connect to your account.
When inviting someone to connect to your account you can define user access levels that control what others can do on your behalf. For example, you can authorise another user to launch and edit a transaction, but only you can submit.
Only a user with Senior administrator or Administrator Access level for an entity can invite other users to connect to that entity.
For information on how to invite someone to connect to your account and user access levels, see the Administration section on the FAQ page.